
Security research and disclosures
Vulnerability research, disclosure write-ups and practical hardening guidance for people running WordPress in production.
-
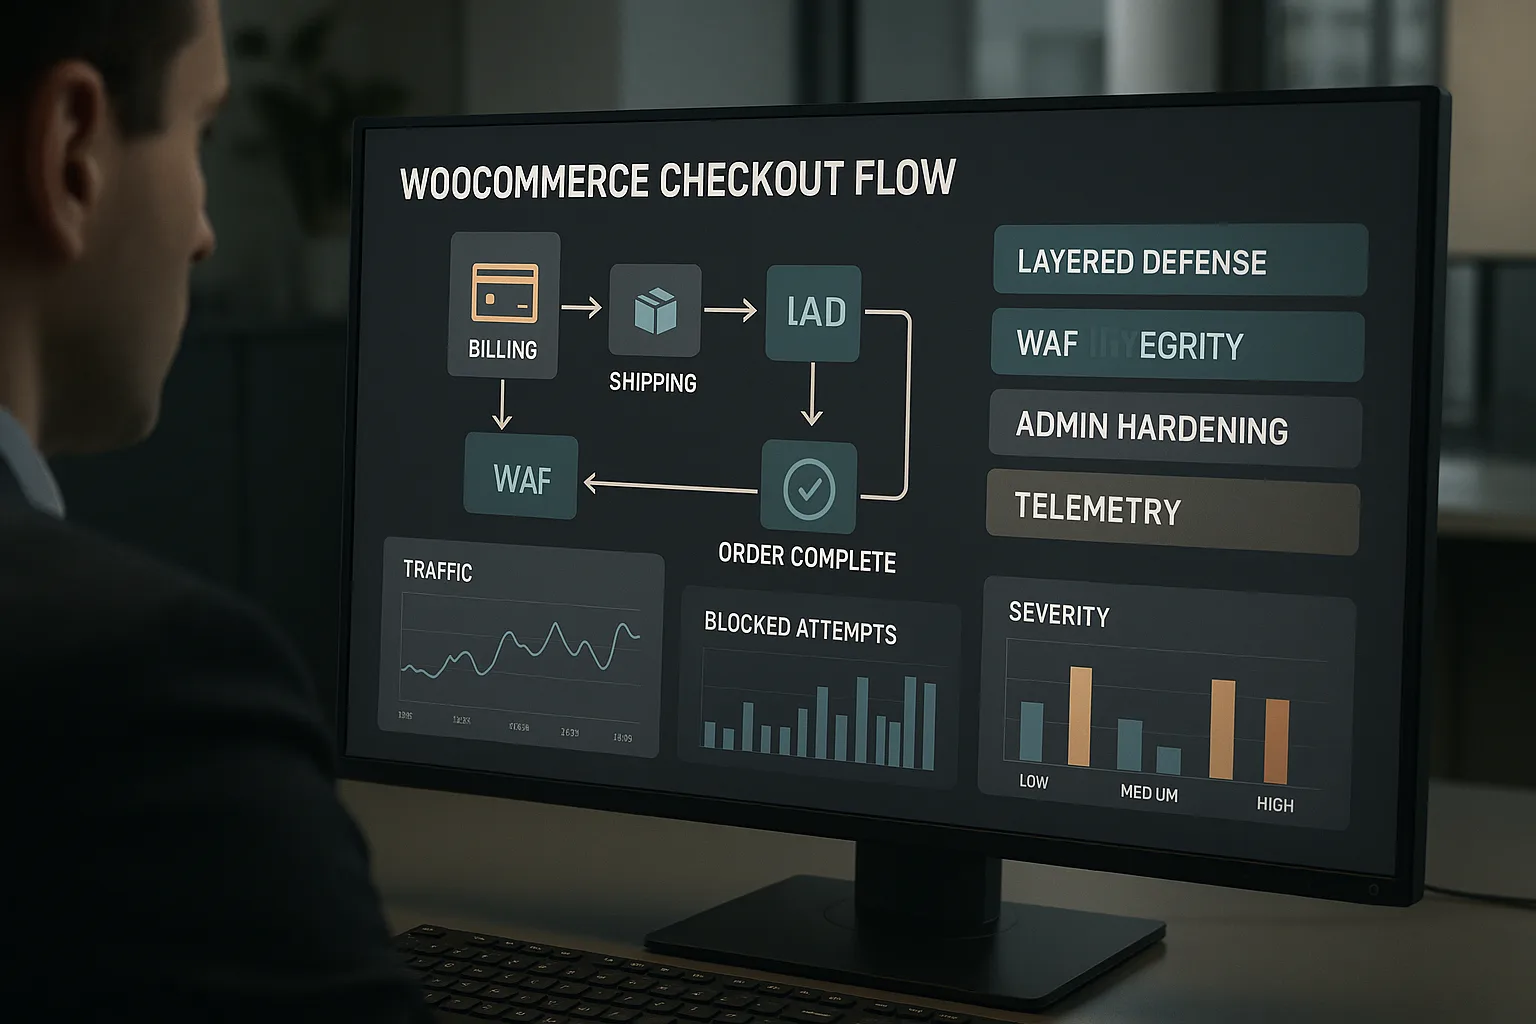
Teardown: Mistakes That Let Malware and Web Shells Reach WooCommerce Checkouts — A Layered-Defense Fix
A tactical operator teardown for eCommerce managers: common mistakes that let malware and web shells touch WooCommerce payment flows, plus corrective actions to build…
-
Layered Defense Teardown: Avoiding the Mistakes That Let Malware and Web Shells Reach WooCommerce Checkouts
A tactical teardown for eCommerce managers: common operational mistakes that allow malware and web shells into WooCommerce checkout flows, with corrective actions and monitoring…
-
Mistakes eCommerce Managers Make When Defending WooCommerce from Malware and Web Shells — A Tactical Teardown
An operator-focused teardown for eCommerce managers: common mistakes that let malware and web shells reach checkout flows, with corrective actions and layered controls you…
-
Why Other Plugins Aren’t Enough: Hardening Admin Access and Privileged Workflows
A step-by-step Operator Notes blueprint for agency operators: why relying on generic plugins leaves admin access exposed, and how to implement layered controls that…
-
Reduce Plugin Exploit Risk Before Disclosure: A Battle-Tested Checklist Playbook
A pragmatic, battle-tested checklist for WordPress site owners to shrink the plugin exploit window between disclosure and patch — practical controls you can apply…
-
Stopping Brute-Force & Credential Stuffing: A Practical Hardening Roadmap for IT Operators
A practical, prioritized roadmap for IT generalists to stop brute-force and credential stuffing attacks on WordPress sites. Quick wins, detection steps, and deep fixes…