
Security research and disclosures
Vulnerability research, disclosure write-ups and practical hardening guidance for people running WordPress in production.
-
Fight Back: A Step-by-Step Operator Blueprint to Stop Brute-Force & Credential Stuffing
A mentor-style, step-by-step blueprint for agency operators to stop brute-force and credential stuffing across multiple client WordPress installs, with practical detection, hardening, checklist, and…
-
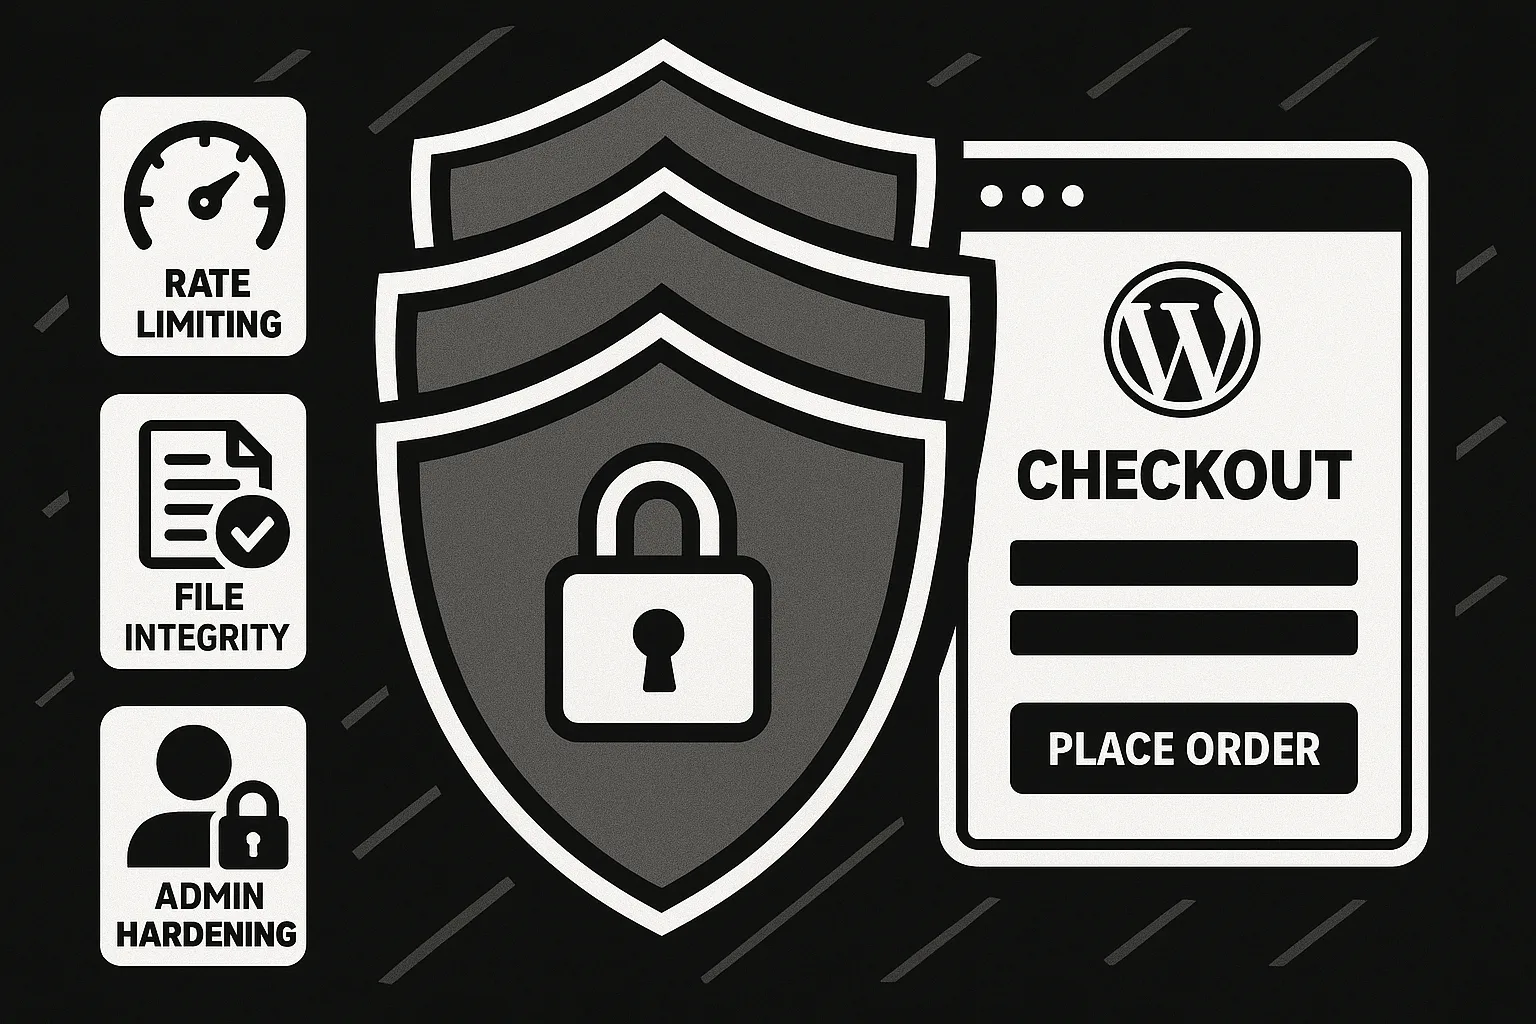
Playbook: Defend High-Value Content and Checkout Flows from Automated Abuse
A pragmatic, battle-tested checklist playbook for WordPress owners to stop automated abuse targeting high-value content and checkout flows — practical controls you can implement…
-
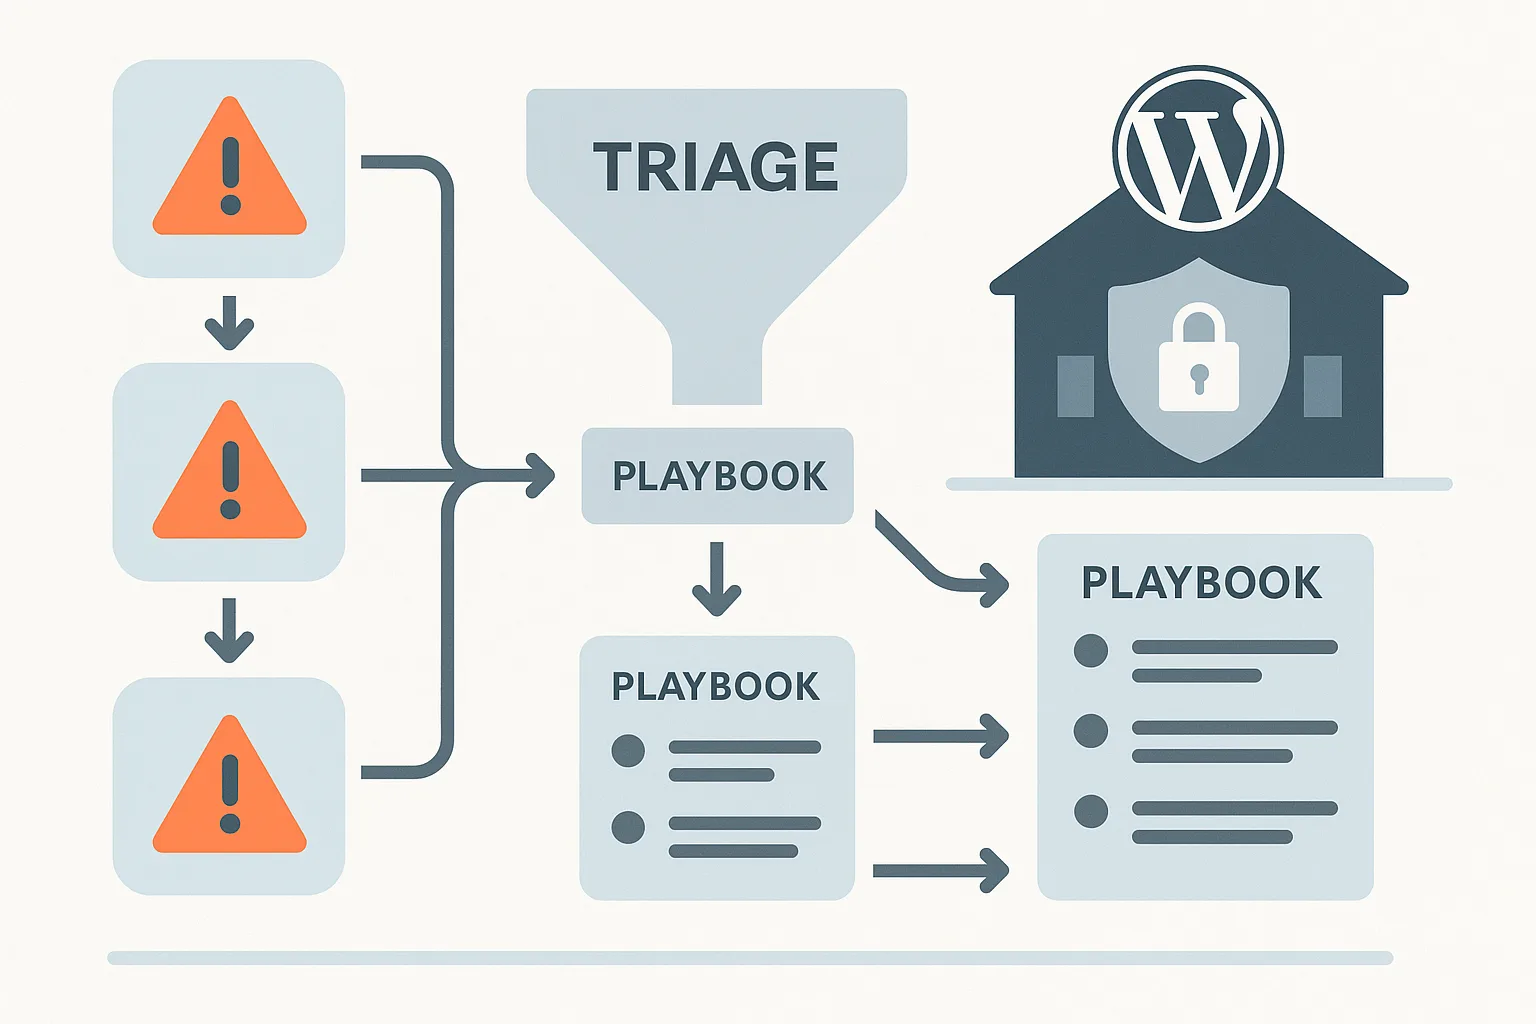
How WordPress Hacks Actually Happen — A Roadmap to Turn Noisy Telemetry into Concrete Remediation
An implementation roadmap for IT generalists: stop letting noisy WordPress alerts hide real compromises. Quick wins, deep fixes, and playbooks that convert telemetry into…
-
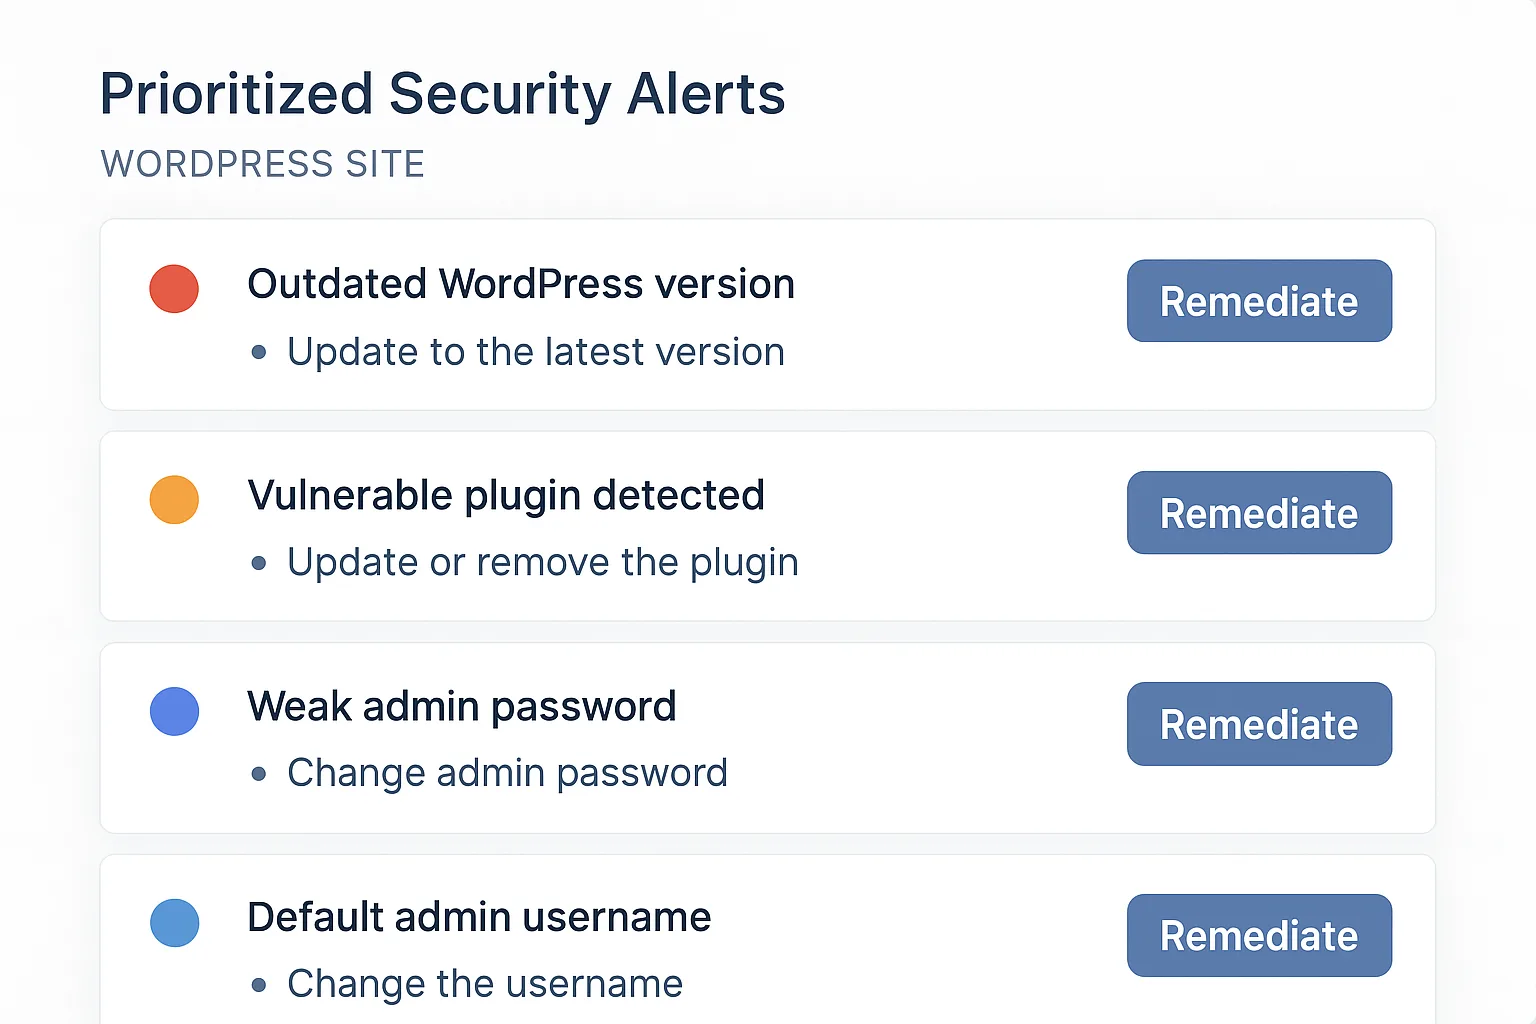
How WordPress Hacks Actually Happen: Turning Noisy Telemetry into Concrete Remediation
A hardening guide for IT generalists: map noisy WordPress telemetry to concrete short-term wins and deep fixes so you stop triage thermometers and start…
-
How WordPress Hacks Unfold: Turning Noisy Telemetry into Concrete Remediation
A practical hardening guide for IT generalists: map noisy WordPress alerts to fast remediation, quick wins for uptime, and deeper fixes to prevent recurring…
-
Reduce Incident Blast Radius: A Tactical Threat-Model Walkthrough for WordPress Founders
A high-urgency, prioritized threat-model walkthrough showing how technical founders can harden WordPress, monitor effectively, and build recovery playbooks that limit damage when a site…