
Security research and disclosures
Vulnerability research, disclosure write-ups and practical hardening guidance for people running WordPress in production.
-
Fight Back: Hardening Admin Access and Privileged Workflows — An Implementation Roadmap
A tactical, implementation-focused roadmap for IT generalists: quick wins to reduce attack surface and deeper fixes to secure WordPress admin and privileged workflows.
-
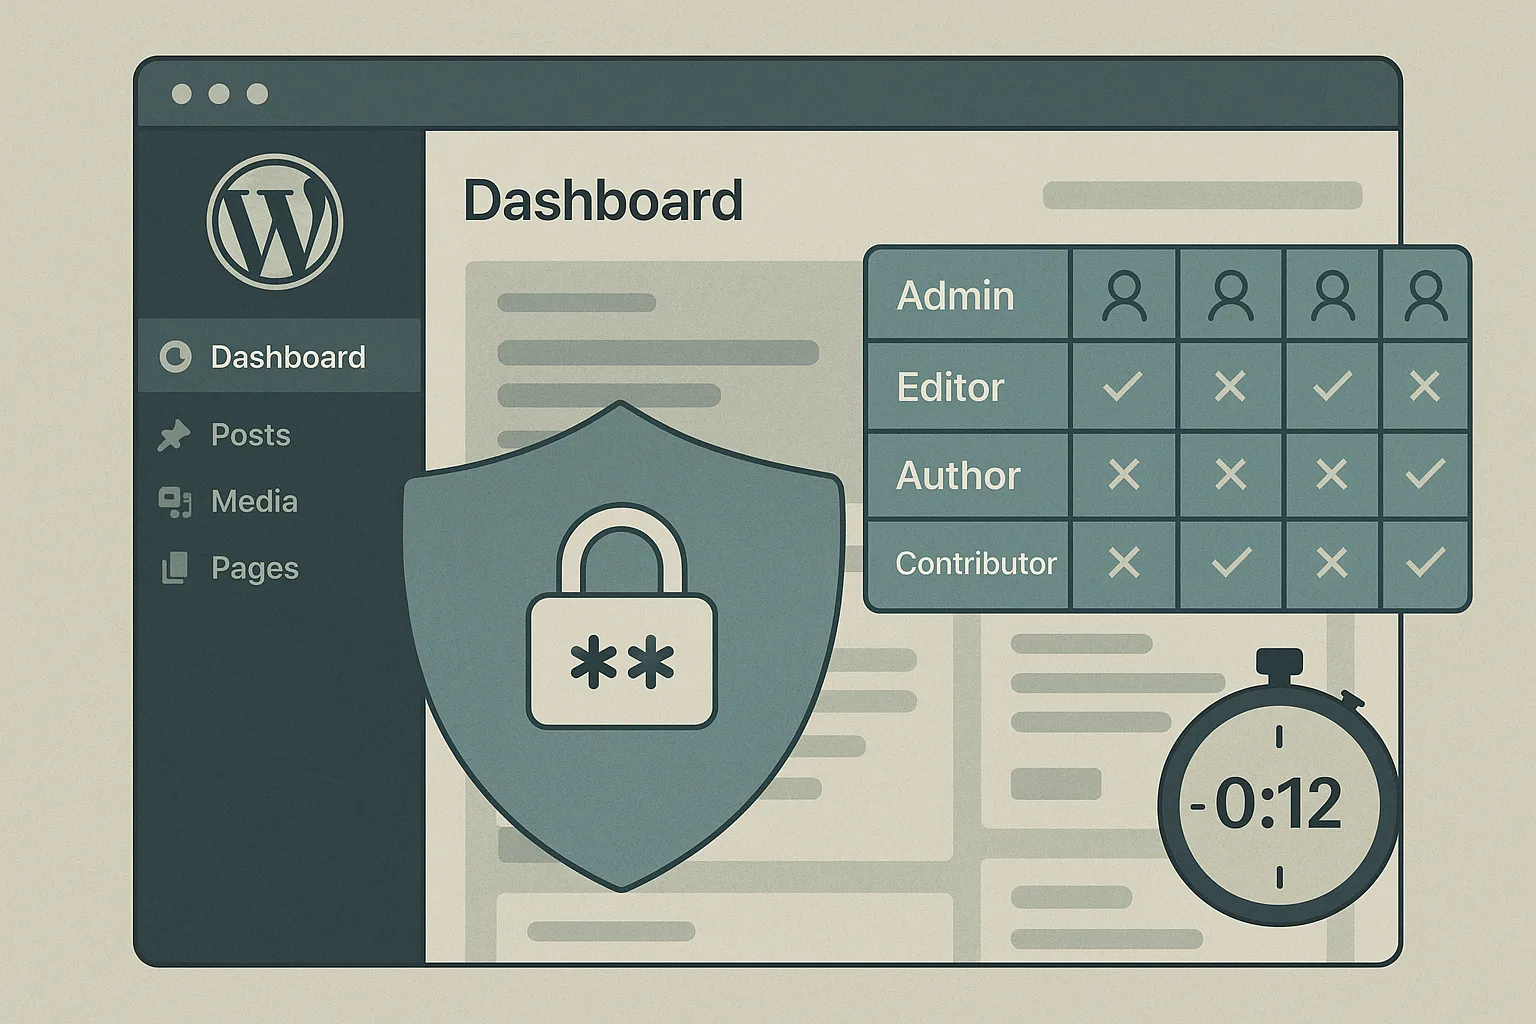
Hardening Admin Access and Privileged Workflows: A Practical Roadmap for IT Operators
A hands-on roadmap for IT generalists to harden WordPress admin access and privileged workflows: quick wins you can deploy in hours, deep fixes for…
-
Reduce Plugin Exploit Risk Before Disclosure: A Founder’s Fast Threat-Model Walkthrough
A high-urgency, technical founder’s playbook to shrink the exploit window when a plugin vulnerability is about to be disclosed. Prioritized defensive controls you can…
-
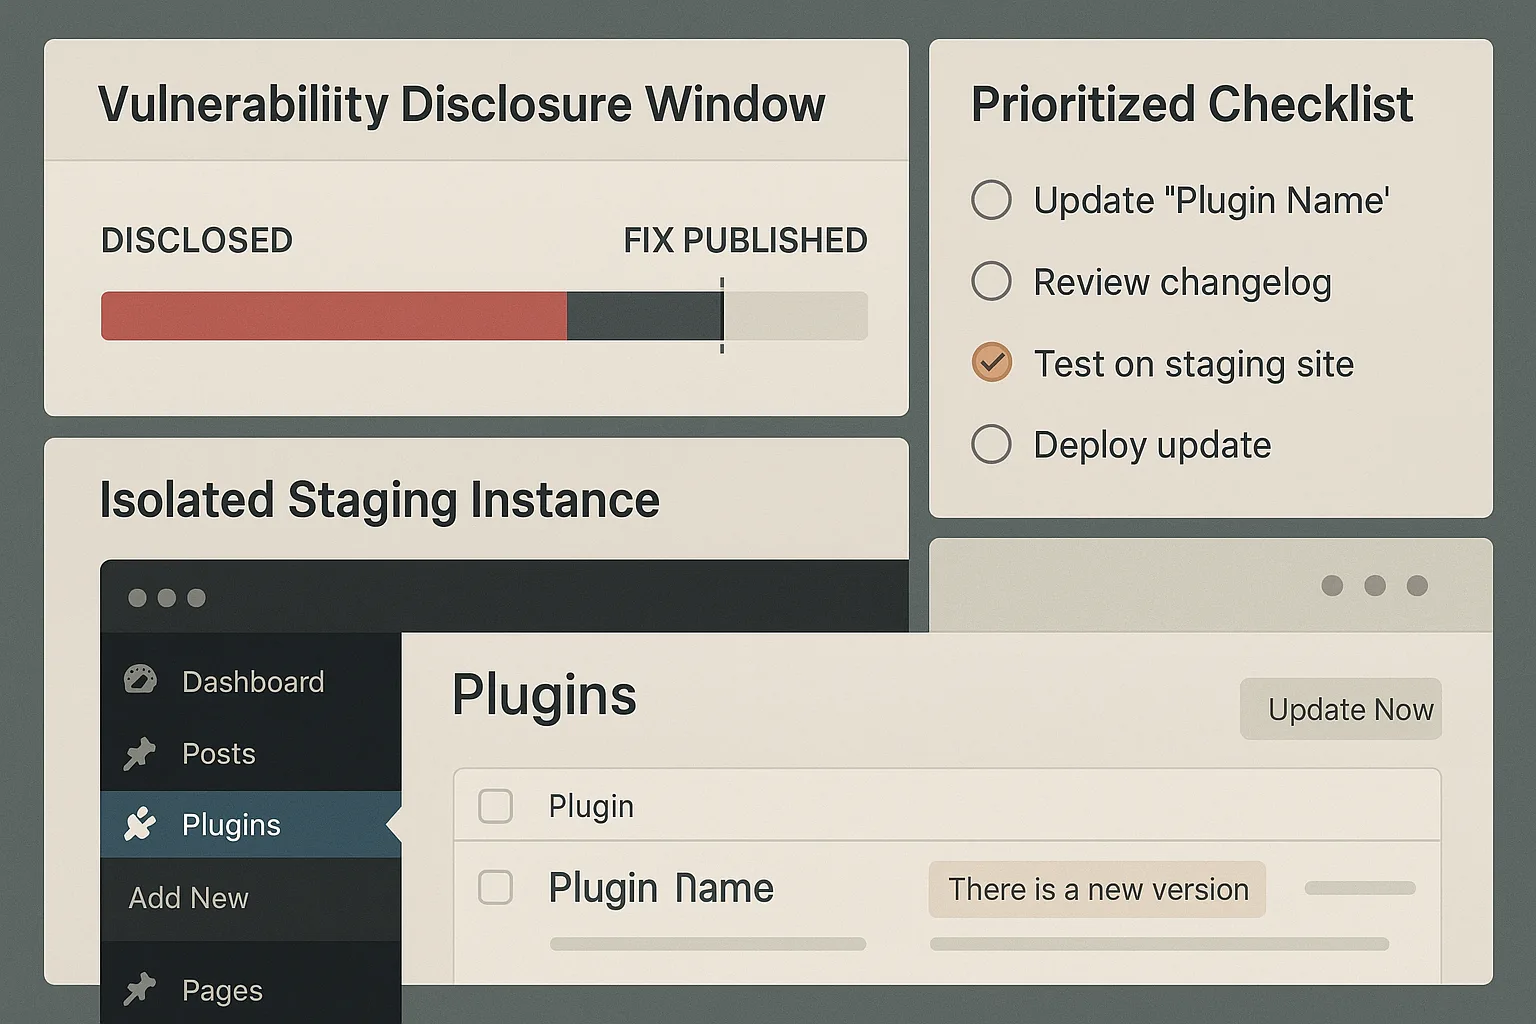
Reduce Plugin Exploit Risk Before Disclosure: A Threat-Model Walkthrough for Founders
A high-urgency, tactical threat-model walkthrough for technical founders: prioritized defensive controls to reduce plugin exploit risk in the crucial window between discovery and public…
-
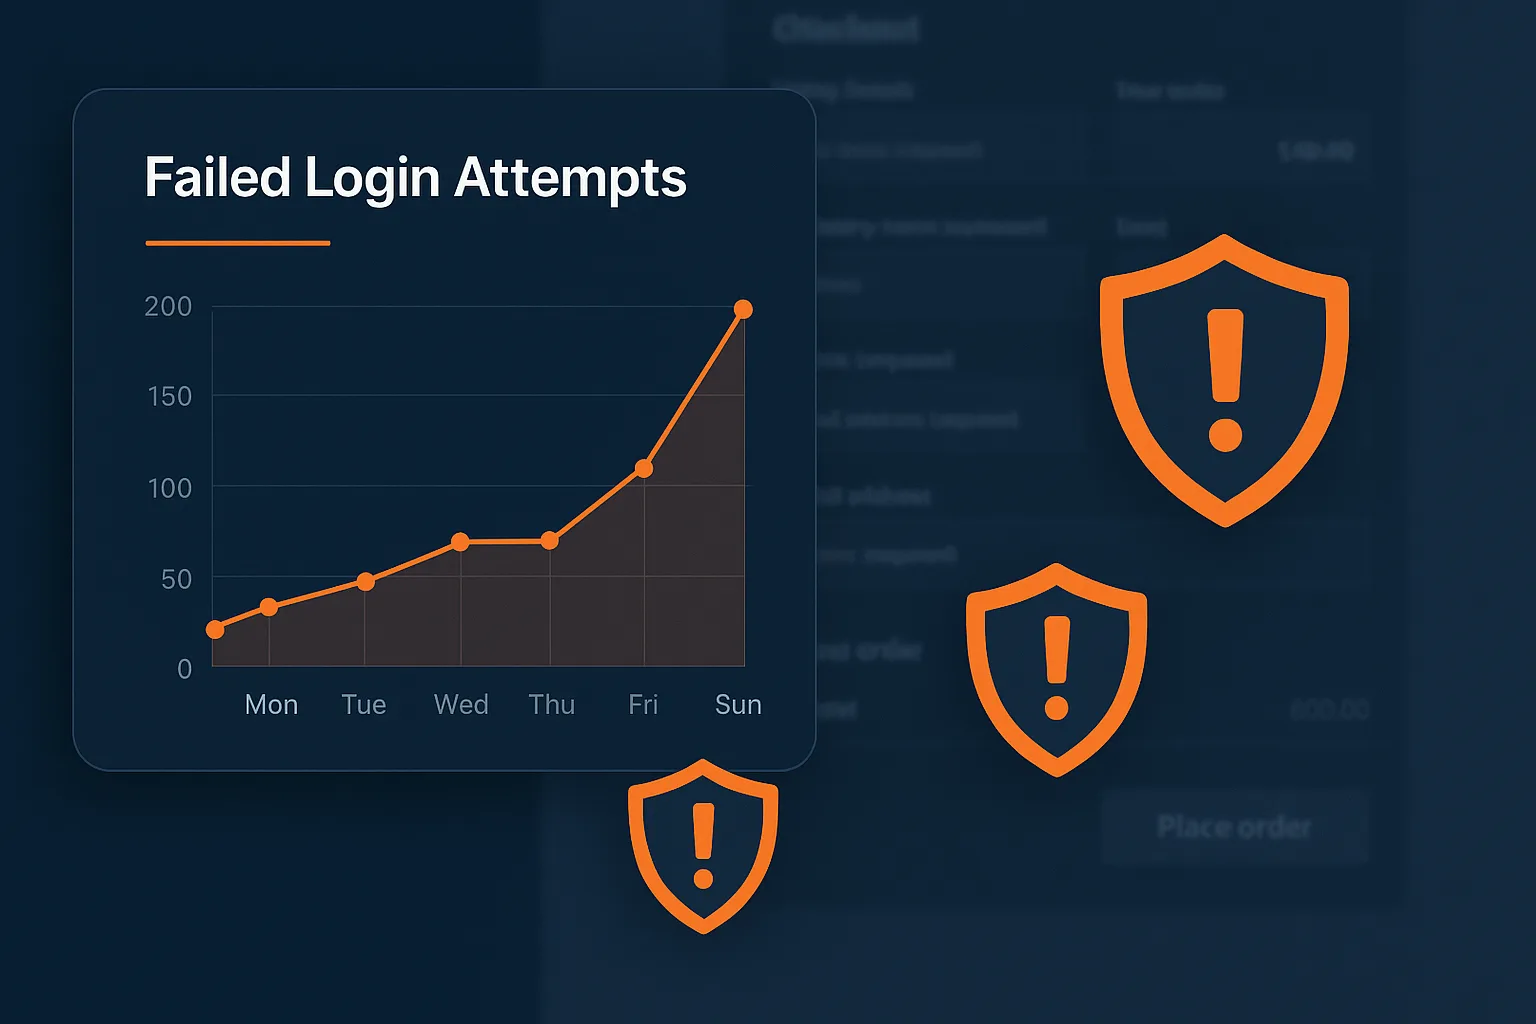
How WordPress Hacks Actually Happen: A Tactical Teardown to Stop Brute-Force & Credential Stuffing on WooCommerce
An operator-focused mistakes-to-avoid teardown for eCommerce managers: learn how brute-force and credential stuffing bypass WooCommerce protections, the specific mistakes that invite them, and the…
-
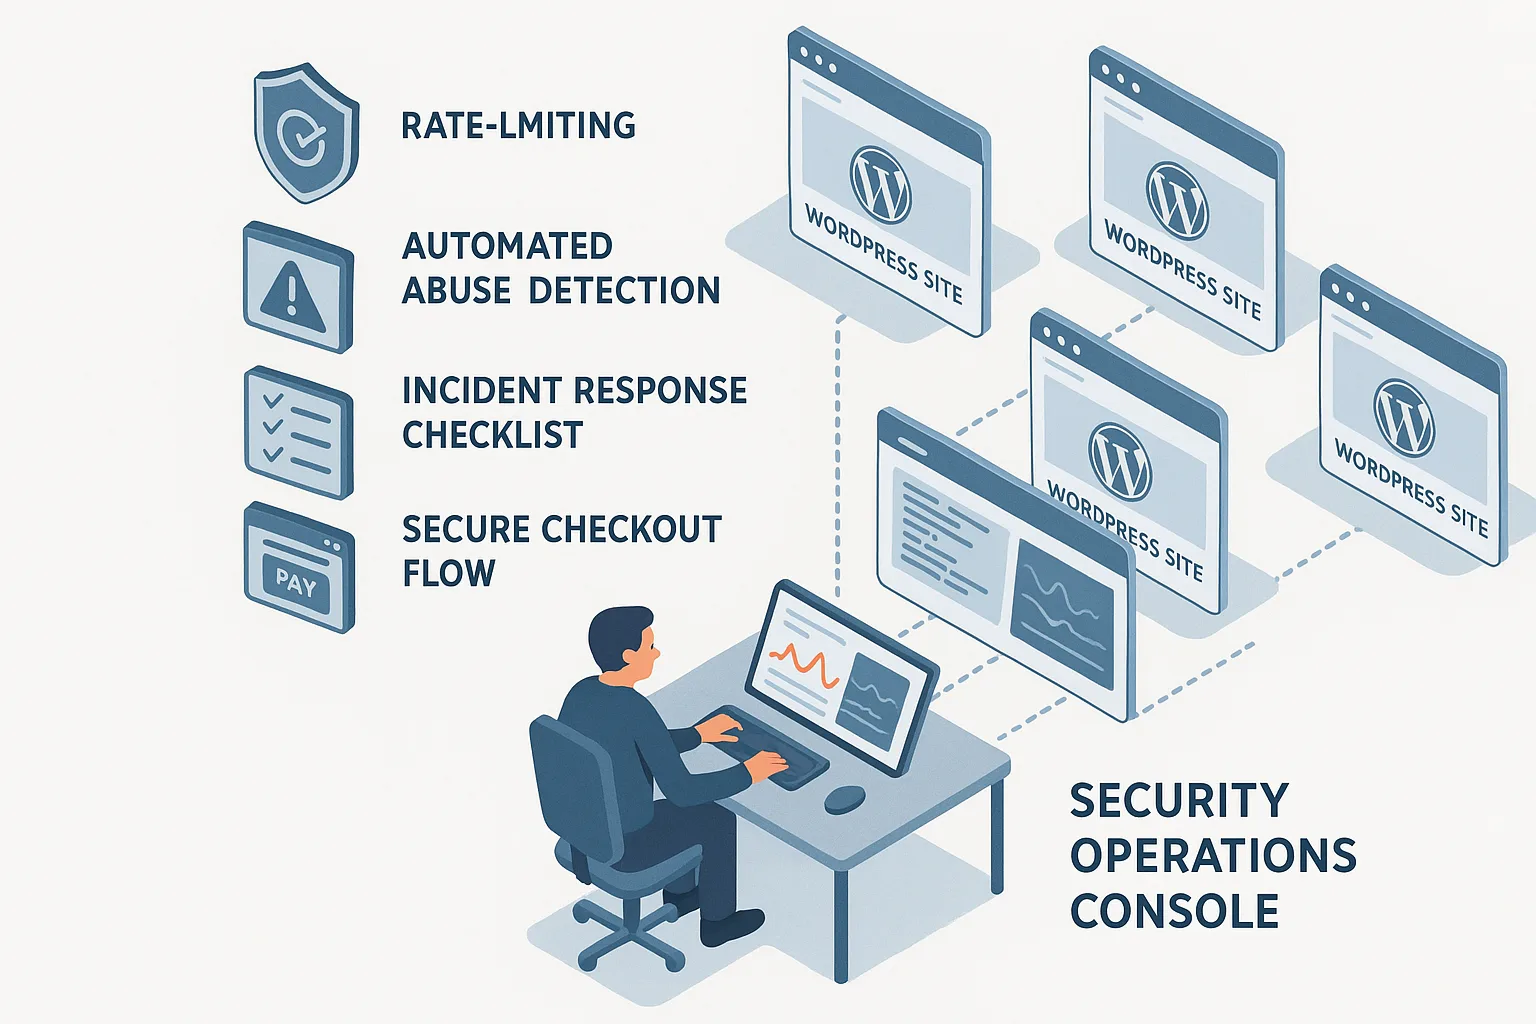
Operator Blueprint: Defend High-Value Content & Checkout Flows from Automated Abuse
A step-by-step operator blueprint for agencies to harden WordPress sites and respond to automated abuse targeting gated content and checkout flows. Practical controls, detection…