
Security research and disclosures
Vulnerability research, disclosure write-ups and practical hardening guidance for people running WordPress in production.
-
Reduce Plugin Exploit Risk During Disclosure Windows: An Incident-Focused Hardening Roadmap
A practical, prioritized hardening roadmap for IT generalists to reduce plugin exploit risk during disclosure windows — quick triage actions, deep fixes, and an…
-
Why Other Plugins Aren’t Enough: A Threat-Model Walkthrough to Stop Brute-Force & Credential Stuffing
A tactical, prioritized threat-model walkthrough for technical founders: why many WordPress plugins miss the attacker’s tradecraft and which hardening controls actually stop large-scale brute-force…
-
Why Other Plugins Aren’t Enough: A Threat-Model Walkthrough to Stop Brute-Force & Credential Stuffing
A tactical, high-urgency walkthrough for founders: what makes brute-force and credential stuffing succeed, why common plugin approaches fail, and a prioritized hardening roadmap you…
-
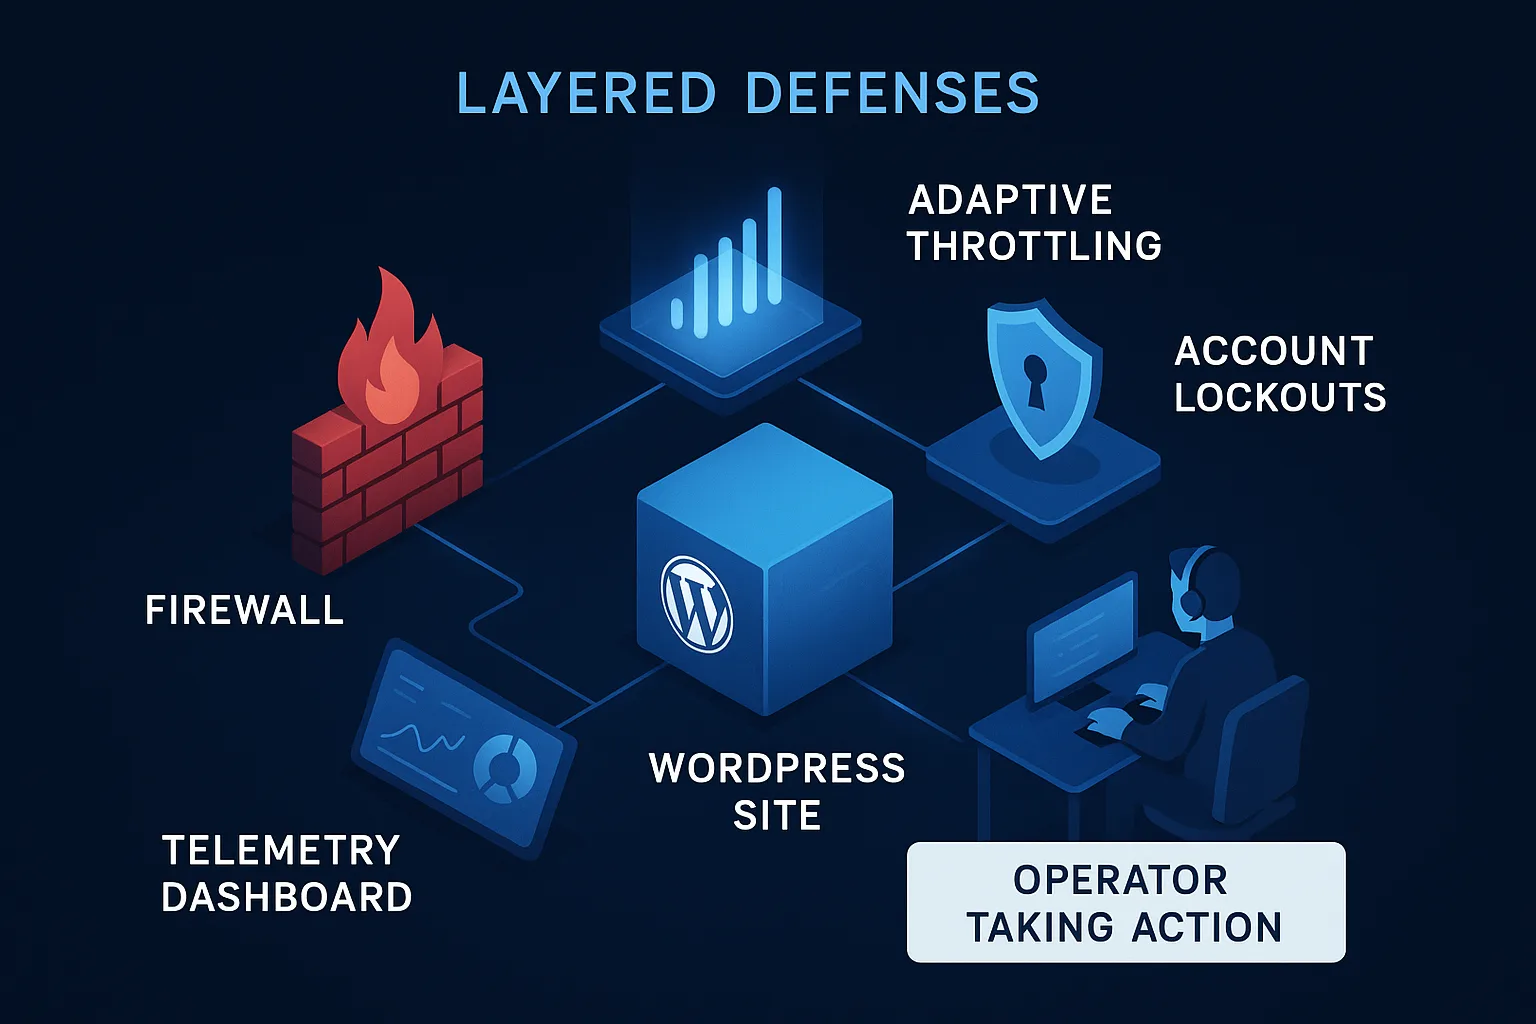
Why Other Plugins Aren’t Enough to Stop Brute-Force & Credential Stuffing
A high-urgency, prioritized threat-model walkthrough for founders: why rate-limit plugins fail against modern credential-stuffing and what layered controls you must deploy now — with…
-
Fight Back: Teardown — Mistakes eCommerce Managers Make Defending WooCommerce Checkouts from Automated Abuse
An operator-focused teardown for eCommerce managers: the most common mistakes that let automated attackers abuse WooCommerce checkout flows, and the tactical corrective actions to…
-
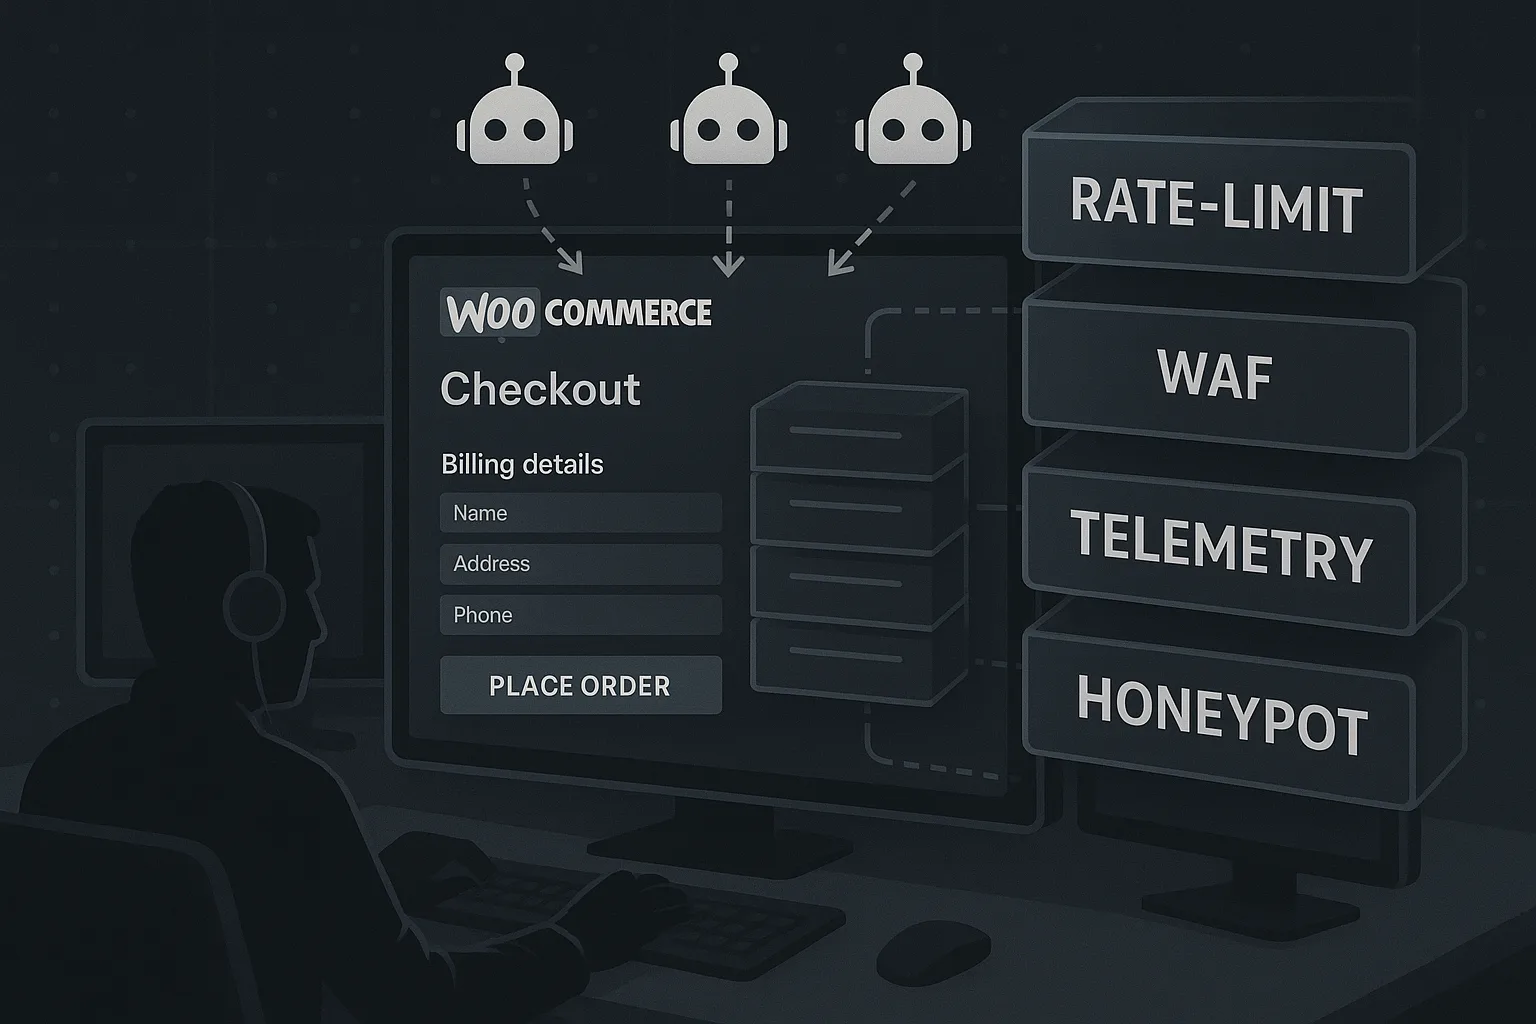
Fight Back: A Tactical Teardown — Stop Automated Abuse Targeting WooCommerce Checkouts
An operator-focused teardown for eCommerce managers: the common mistakes that let bots, credential stuffing, and web shells affect checkout flows — and exact corrective…