
Security research and disclosures
Vulnerability research, disclosure write-ups and practical hardening guidance for people running WordPress in production.
-
Fight Back: A Tactical Layered Defense Against WordPress Malware and Web Shells
A high-urgency, prioritized threat-model walkthrough for technical founders: practical controls to prevent, detect, contain and recover from WordPress malware and web shell attempts without…
-
Fight Back: Layered Defense Against WordPress Malware & Web Shells
A high-urgency, prioritized walkthrough for founders: model attacker behavior, then build layered prevention, detection, and rapid containment controls to stop malware and web shells…
-
Admin Privilege Mistakes eCommerce Managers Make — A Tactical Teardown to Protect WooCommerce Payments
A practical, operator-focused teardown showing common admin-access mistakes that expose WooCommerce payments and customer data, with precise corrective actions you can apply today.
-
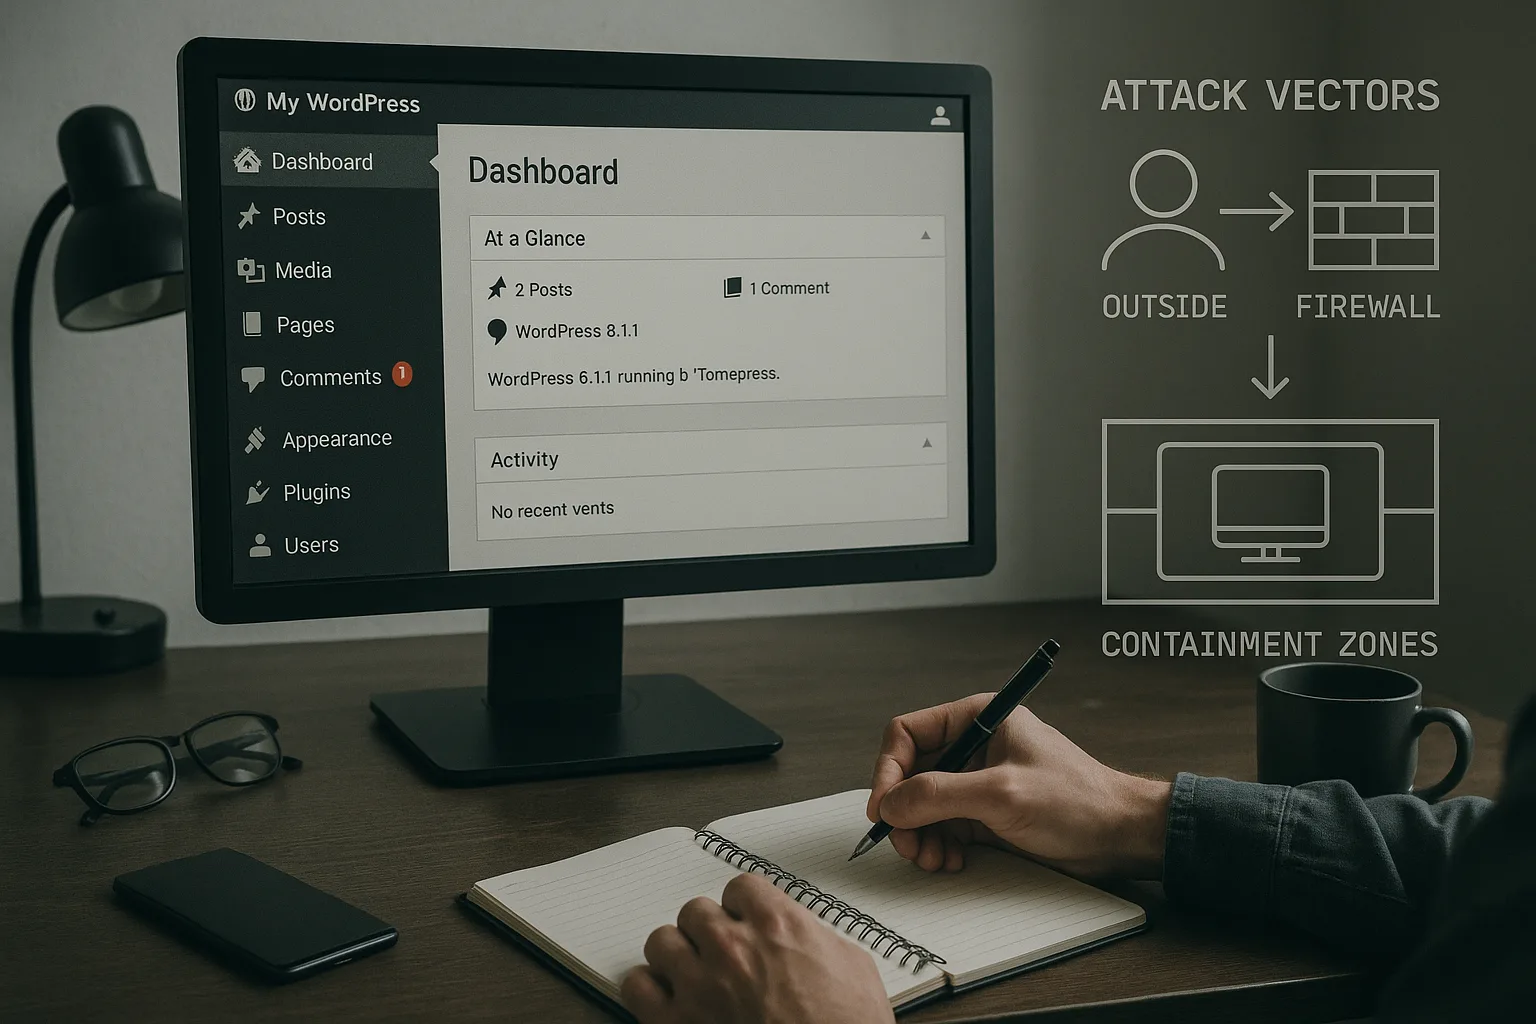
How WordPress Hacks Actually Happen: An Operator Blueprint to Reduce Plugin Exploit Risk
A practical, step-by-step blueprint for agencies to reduce plugin exploit risk across client WordPress installs—fast triage, containment and fleet-wide hardening before disclosure windows close.
-
How WordPress Hacks Actually Happen: An Operator Blueprint to Reduce Plugin Exploit Risk
A step-by-step operator guide that explains how WordPress plugin exploits move from discovery to mass compromise — and exactly what agencies should do now…
-
Battle-Tested Playbook: Stop Brute-Force & Credential Stuffing on Your WordPress Site
A pragmatic, battle-tested playbook for WordPress owners to harden login paths, detect credential stuffing, and run fast incident response without a full SOC.